
That gap has been real. ISO/IEC 27001 and 27002 cover information security controls in general. ISO/IEC 42001 covers AI management systems: governance, accountability, impact assessment. None of them tells a security team what a model-specific attack looks like or how to defend against it. 27090 is written to close that gap, and it matters for any organisation that builds, fine-tunes, or simply deploys AI, generative or otherwise.
27090 addresses two areas: the threats your AI systems face, and the security practices that counter them.
The threats it names are specific to how models work: data poisoning, model exfiltration through queries that look legitimate, evasion, membership inference, model inversion, and prompt injection.
The practices it recommends extend established security disciplines to AI:
It is guidance, not a certifiable requirements list, and it assumes conventional controls are already in place underneath it.
27090 does not replace anything you already have. If you are ISO 27001 certified, your ISMS still stands; 27090 gives you the AI-specific guidance to fold into it, much as you would with other sector-specific guidance.
If you are working toward or hold ISO 42001, that standard still owns governance and accountability for the AI management system as a whole; 27090 is the technical security layer underneath it, covering how the system itself gets attacked and defended.
Treat it as an addition to the stack, not another standalone programme: 27001 for the ISMS, 42001 for AI governance, 27090 for AI-specific security practice.
If you develop AI products, or you have fine-tuned or integrated third-party models into anything client-facing, 27090 is worth a read now.
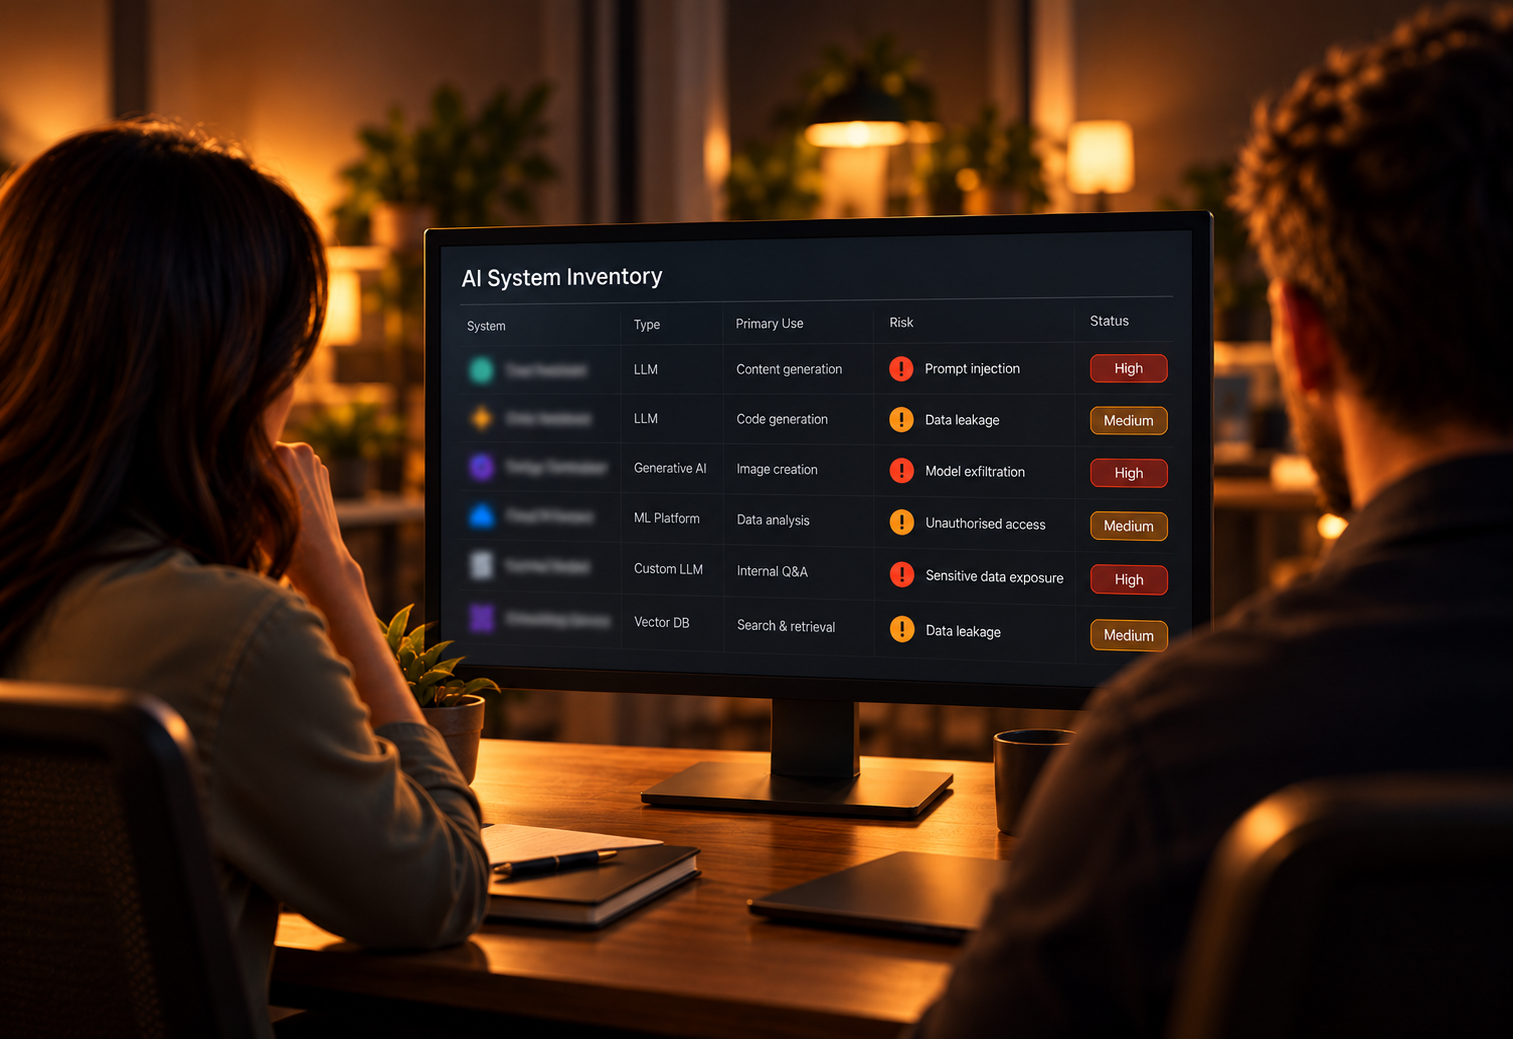
The first useful step: pull your current AI/ML inventory and ask, for each system, whether data poisoning, prompt injection, and model exfiltration appear anywhere in its risk assessment. For many organisations the honest answer right now could be no.
If you only consume AI through vendor tools and have no models of your own, the relevant question shifts to supply chain: does your vendor due diligence ask these questions of the AI vendors you rely on, or does it still treat an AI product like any other piece of SaaS?
Our ISO/IEC 27090 gap analysis service maps the standard against your existing ISO 27001 ISMS, AI governance work or existing controls. You get a clear view of what's new, what's already covered and what's missing. Contact us to arrange an assessment.


